

Working from anywhere has become standard practice for millions of professionals, but the convenience of airport lounges and coffee shops comes with serious security tradeoffs. Public wi fi networks create vulnerabilities that expose your business data, employee credentials, and customer information to cybercriminals who actively hunt for these easy targets. Understanding these risks helps organizations protect their operations while maintaining workforce flexibility.
Key Takeaways
- 43% of public WiFi users have experienced data breaches, with man-in-the-middle attacks and packet sniffing as the most common threats.
- Globally, the average cost of a data breach is now $4.44 million, with U.S. organizations experiencing price tags that commonly exceed $10 million per breach.
- 68% of breaches involve human elements, making employee training and security measures as important as technical protections.
- The healthcare, finance, and retail industries face the highest public WiFi security risks because employees handle sensitive information while on the go.
- Virtual private network services, HTTPS-only browsing, and avoiding financial transactions on public networks represent the core defenses against most attacks.
- 89% of wi fi networks tested contain vulnerabilities that allow attackers to bypass even WPA2 and WPA3 encryption.
What Are the Risks of Using Public WiFi?
The risks of using public wi fi extend far beyond simple password theft. When employees connect to unsecured networks, they expose every piece of data transmitted to potential interception. Public networks at airports, hotels, and restaurants rarely implement proper security measures, leaving business communications vulnerable.
Cybercriminals position themselves on these public wi fi networks specifically to harvest login credentials, financial information, and proprietary business data. The attacks happen silently—most victims don’t realize their sensitive data has been compromised until weeks or months later, when unauthorized transactions appear or company systems show signs of breach.
Business networks face compounding security risks when compromised employee devices later connect to corporate systems. A single infected laptop can introduce malware that spreads across an entire organization. The initial infection point traces back to that coffee shop wi fi connection where an employee checked their email.
Remote workers represent a particular vulnerability. 60% of employees regularly use hotel or airport wi fi for work tasks, often accessing sensitive accounts without adequate protection. This widespread behavior exponentially multiplies organizational risk.
What Makes Public WiFi Dangerous?

Lack of Encryption Standards
Public WiFi networks lack the fundamental security controls that private networks have. Most public hotspots use no encryption or rely on outdated WEP, which attackers can break in seconds. Without proper encryption, all data flows across the network in plain text.
Anyone on the same network can monitor internet traffic. This “shared medium” nature means dozens or hundreds of connected devices transmit data simultaneously through the same access point. Specialized software makes intercepting this traffic trivially easy.
Outdated Infrastructure and Poor Maintenance
Network administrators rarely update public wi fi infrastructure. Many public access points run outdated firmware with known vulnerabilities that attackers routinely exploit. Hotels and restaurants prioritize convenience over security, creating ideal conditions for cyberattacks.
Authentication requirements vary wildly. Some WiFi networks require no password at all, while others use shared passwords that remain unchanged for years. Both scenarios leave users vulnerable to attacks from anyone within wi fi range.
Extended Attack Range
The physical proximity requirement that once limited wi fi attacks no longer applies. Attackers use specialized antennas and techniques to intercept signals from hundreds of meters away, dramatically expanding their potential victim pool.
What Types of Data Are at Risk on Public WiFi?
Public wi fi connections expose multiple categories of sensitive information to potential theft:
- Login credentials: Usernames and passwords for corporate systems, email accounts, cloud services, and financial platforms flow unencrypted across public wi fi networks unless properly protected. 86% of breaches involve stolen or compromised credentials.
- Financial information: Online banking sessions and payment transactions often involve sending credit card and account information that, if intercepted, gives attackers immediate access to financial assets.
- Email communications: Email contents and metadata reveal business operations, client relationships, and strategic plans. Attackers harvest email communications to build intelligence profiles or launch targeted phishing campaigns.
- Proprietary documents: File transfers expose sensitive documents, customer databases, and intellectual property through cloud storage synchronization, document sharing, and remote access sessions.
- Session tokens: Session cookies and authentication tokens can be hijacked by attackers to hijack active login sessions. These temporary credentials let criminals impersonate legitimate users without needing actual passwords, bypassing multi-factor authentication in many cases.
- Network access information: Corporate network access information provides pathways into your business systems. VPN configurations, network topology details, and internal resource locations help attackers plan sophisticated intrusions.
What Are the Most Common Cyber Attacks on Public WiFi?

1. Man-in-the-Middle (MITM) Attacks
Man-in-the-middle attacks position cybercriminals between your device and the internet. The attacker intercepts all traffic, reads or modifies data, and relays it to the intended destination. MITM attacks account for 19% of successful cyberattacks in 2024.
Attackers execute mid-level attacks by compromising the access point itself or by positioning themselves on the WiFi network to capture passing traffic. Your device communicates normally, showing no obvious signs of compromise, while attackers harvest everything you send and receive.
These attacks bypass many security measures. Even if you type your password into a legitimate website, the attacker captures it as the data crosses the compromised network. The website receives your login credentials, you gain access to your online accounts as usual, and you remain unaware of the breach.
Advanced MITM techniques can even intercept HTTPS traffic through SSL stripping. Attackers downgrade your secure connection to plain HTTP, making encryption ineffective. Your browser may display subtle warnings in the address bar, but most users miss these indicators.
Research shows that 89% of WiFi networks tested contain vulnerabilities that enable MITM attacks that bypass WPA2 and WPA3 encryption. Even networks that appear secure may not protect against determined attackers with the right tools.
2. Packet Sniffing and Eavesdropping
Packet sniffing involves capturing data packets as they travel across networks. Free tools like Wireshark make packet sniffing accessible to attackers with minimal technical knowledge. These tools display all unencrypted data flowing across a network in a readable format.
Attackers positioned on public WiFi networks run packet sniffers continuously, automatically collecting credentials, email content, and other sensitive information. The process requires no sophisticated techniques—just patience and basic software.
One research study monitoring unsecured WiFi networks in Japan captured unencrypted photos, documents, emails, and credentials in just 150 hours. All harvested data appeared in plain text, ready for immediate data theft.
Packet sniffing is particularly effective against websites that still use HTTP instead of HTTPS. While major sites now use encryption, many smaller business applications and internal tools lack proper security software. Employees accessing these systems expose credentials instantly.
The technique works passively, leaving no traces on victim devices. Unlike malware that security software might detect, packet sniffing happens entirely on the network, invisible to endpoint protection systems.
3. Rogue WiFi Networks (Evil Twin Attacks)
Evil twin attacks involve creating fake wi fi networks that mimic legitimate networks. An attacker sets up a hotspot named “Airport Free WiFi” or “Hotel Guest Network” with a stronger signal than the real network. Unsuspecting users connect to the fake hotspot, believing they’re joining the legitimate service.
Once connected to an evil twin network, all your traffic flows through the attacker’s device. They have full control over every aspect of your internet connection, monitoring communications, injecting malware, or redirecting you to fake websites that harvest credentials.
These attacks require minimal equipment—often just a laptop and readily available software. Attackers position themselves in coffee shops, airports, or hotels where people expect free WiFi. A stronger signal from the fake network often causes devices to connect to it automatically.
Evil twins become particularly dangerous with captive portals requesting login credentials. Users who enter their email and password to “activate” the WiFi actually hand their credentials directly to attackers, who then test them against corporate systems.
4. Session Hijacking
Session hijacking involves stealing active login sessions rather than passwords. When you connect to a website or application, the server issues a session token that proves your identity for subsequent requests. Attackers who capture this token can impersonate you without needing your password.
These attacks are especially effective against public WiFi, where session tokens are often transmitted without encryption. Public WiFi networks create prime conditions for session hijacking because many applications fail to adequately protect these tokens.
Session hijacking bypasses multi-factor authentication in many implementations. If MFA only verifies at initial login, stolen session tokens provide full access for their entire validity period—often hours or even days.
Attackers use session hijacking to commit financial fraud, access corporate systems, and read personal messages. The 2010 Firesheep Firefox extension demonstrated how easily anyone could hijack sessions on unsecured networks, forcing major websites to adopt stronger protections.
The technique requires specific timing—attackers must capture the session token during its active period. Public wi fi environments provide ideal conditions because victims remain connected for extended periods, giving attackers ample opportunity.
5. Malware Distribution
Public wi fi networks serve as malware distribution vectors in several ways. Compromised access points can automatically inject malware into unencrypted web traffic, infecting devices without user interaction. Attackers also use fake WiFi hotspots to prompt users to download malware.
Ransomware attacks increasingly leverage public wi fi networks as initial infection points. Attackers scan connected devices for vulnerabilities, deploying ransomware that encrypts files and demands payment. North America accounted for 59% of observed ransomware attacks in 2024, with unsecured WiFi networks playing a significant role.
Mobile devices face particular malware infection risks. Fake system update alerts with data-exfiltration capabilities target Android devices specifically, tricking users into installing malware that appears legitimate.
Public WiFi enables file-sharing attacks, where malware spreads automatically to connected devices with file sharing enabled. If even one device becomes compromised, it can use network file shares to push malware to other systems on the network.
The malware often remains dormant initially, activating only after the device connects to corporate networks. This delayed execution helps attackers bypass initial security scans and establish persistent access to business systems.
Which Industries Are Most Vulnerable to Public WiFi Attacks?
- Healthcare organizations face the highest breach costs, averaging $7.42 million per incident, making them prime targets. Medical professionals frequently access patient records, insurance information, and treatment plans while traveling between facilities or working remotely.

Healthcare’s vulnerability stems from the sensitive information that employees handle. HIPAA violations carry severe penalties, and data breaches that expose patient data trigger costly notification requirements and regulatory investigations.
The healthcare industry ranks third among the most attacked sectors globally, with ransomware attacks growing by 25% year over year. Remote access to electronic health records via public WiFi creates exposure points that attackers routinely exploit.
- Financial services rank second-highest in device risk scores, according to 2025 research. Financial professionals access trading platforms, client portfolios, and transaction systems that contain extremely valuable data. A single compromised session can enable unauthorized transfers or trades worth millions.
- Retail businesses handle payment card data and customer purchase histories that attract cybercriminals. Access to point-of-sale systems via public WiFi exposes credit card processing infrastructure to attacks. The retail sector faces particularly high public WiFi security risks due to the remote management of multiple store locations.
- Government agencies encounter unique security risks from espionage and nation-state actors. Employees accessing classified or sensitive government systems through public networks create national security vulnerabilities. Government data breaches often have implications far beyond immediate financial costs.
- Manufacturing companies face risks of intellectual property theft. Engineers and designers accessing CAD files, production specifications, or proprietary formulas through public wi fi expose trade secrets. Industrial espionage through compromised wi fi hotspot connections represents a growing threat.
- Educational institutions struggle to support thousands of users with limited cybersecurity budgets. Faculty and staff accessing student records, research data, and administrative systems through public wi fi create numerous vulnerability points.
What Are the Business Consequences of Public WiFi Security Breaches?
- Global data breaches cost an average of $4.44 million as of 2025, with detection and containment, notification, lost business, and post-breach response driving these expenses. U.S. companies face even steeper costs at $10.22 million per incident, a 9% increase from 2024.

Direct financial losses include regulatory fines, legal fees, and customer compensation. Cybercrime costs globally reach $10.5 trillion annually, with public wi fi breaches contributing significantly to this figure. These costs grow at 15% per year, outpacing most business revenue growth.
Operational downtime disrupts business functions when breached systems require shutdown for investigation and remediation. Organizations taking more than 200 days to identify and contain breaches pay approximately $5.01 million, compared to $3.87 million for faster responses.
- Customer trust erosion represents a less quantifiable but equally devastating consequence. Data breaches exposing customer data drive clients to competitors and damage brand reputation for years. E-commerce and SaaS businesses see immediate subscriber cancellations following breach announcements.
- Legal liabilities multiply when breaches involve regulated data types. GDPR violations carry fines up to 4% of global annual revenue, while HIPAA penalties can reach $1.5 million per violation type per year. Class action lawsuits from affected customers add millions more in legal costs.
- Competitive disadvantage emerges when breaches expose trade secrets or strategic plans. Intellectual property theft enables competitors to access years of research and development, negating the competitive advantages that require substantial investment.
- Employee productivity suffers during and after security incidents. IT teams focus on breach response rather than strategic initiatives, while other employees cannot access necessary systems during remediation efforts when working remotely.
- Insurance premiums increase following breaches, with some organizations becoming uninsurable. Cyber insurance carriers now scrutinize security practices closely, denying coverage or charging prohibitive rates for companies with poor wi fi security policies.
- Regulatory scrutiny intensifies after breaches, with agencies conducting audits and imposing ongoing compliance requirements. The administrative burden of satisfying regulators diverts resources from revenue-generating activities.
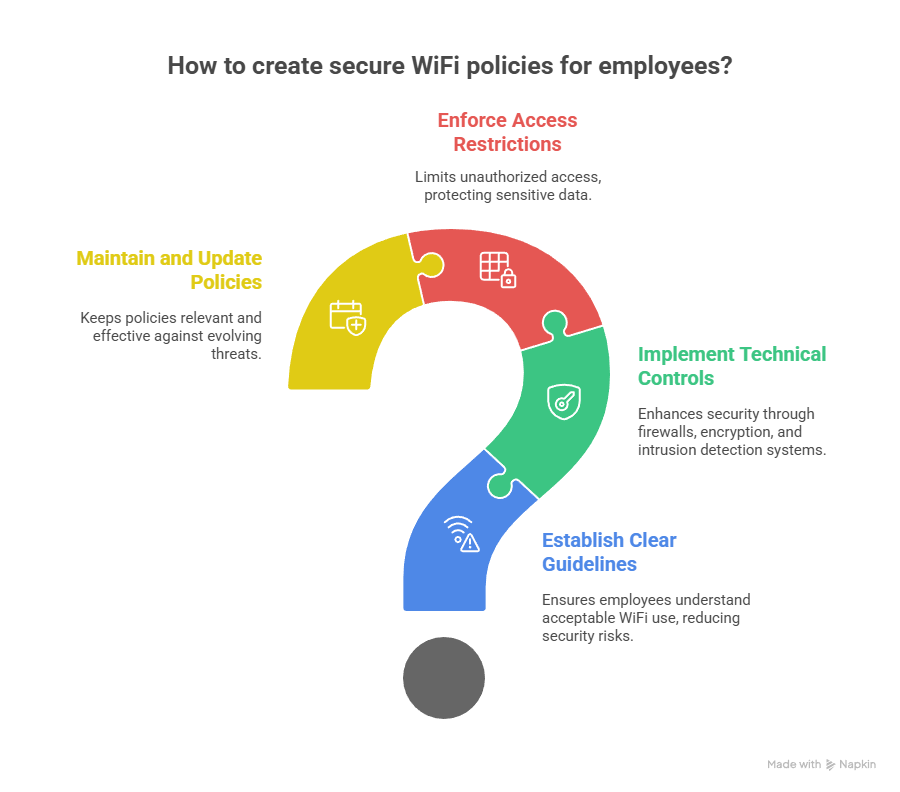
How Should Businesses Create Secure WiFi Policies for Employees?
Establish Clear Usage Guidelines
Comprehensive WiFi security policies begin with clear guidelines on acceptable network use. Policies should explicitly prohibit accessing sensitive systems, conducting financial transactions, or transmitting confidential data over public WiFi unless approved security measures are in place.
Employee training programs must specifically address public WiFi security risks. Generic cybersecurity awareness isn’t sufficient—employees need practical instruction on identifying secure networks, recognizing fake wi fi networks, and using security tools properly.
Implement Technical Controls
Virtual private network requirements form the cornerstone of effective policies. Organizations should mandate the use of VPN services for all public network connections and provide employees with enterprise virtual private network solutions that automatically activate when connecting to untrusted networks.
Device management policies should require automatic security updates, endpoint protection software, and configuration restrictions. Devices accessing company systems must meet minimum security standards, including a firewall enabled, current antivirus software, and disabled file sharing.
Alternative connectivity options reduce reliance on public WiFi. Companies can reimburse employees for mobile hotspot data plans or provide dedicated hotspot devices. Cellular connections offer significantly better security than public wi fi for most use cases.
Enforce Access Restrictions
Network access controls limit what employees can reach from public networks. Implementing zero-trust architecture ensures that even compromised credentials provide minimal access to critical systems.
Incident response procedures specific to public WiFi compromises help organizations respond quickly. Employees should know exactly whom to contact and what steps to take if they suspect their connection has been compromised.
Maintain and Update Policies
Regular policy reviews ensure guidelines remain current as security risks evolve. WiFi security requires constant updates to keep pace with new attack techniques and evolving protection technologies.
Documentation and acknowledgment processes prove employees understand policies. Requiring an annual policy review and signature creates accountability and provides legal protection for the organization.
Remote work location restrictions may be necessary for highly sensitive operations. Some business functions cannot be conducted safely over public networks, regardless of security measures.
What Are the Best Practices for Safer Browsing on Public Networks?
When you must use public wi fi, implement these protective measures to minimize your risk:
- Always use a VPN: A VPN secures your connection by encrypting all traffic between your device and its server, making local network surveillance ineffective. VPNs create secure connections even through compromised networks, protecting data from packet sniffing and man-in-the-middle attacks.
- Verify HTTPS connections: Look for the padlock symbol in your browser’s address bar and ensure URLs begin with “https://” rather than “http://”. HTTPS encrypts communications between your browser and websites, protecting data even on unsecured networks.
- Disable auto-connect: Turn off auto-connect features on all devices. Manual network selection gives you control over when and where you connect, preventing evil twin attacks that exploit automatic connection behaviors.
- Turn off file sharing: Disable file sharing before connecting to any public network. File sharing enabled on public wi fi allows anyone on the same network to browse, read, or modify files on your device.
- Avoid sensitive activities: Online banking, online shopping, accessing medical records, or working with confidential business data should wait until you reach a secure network. If urgent access is required, use cellular data through a personal mobile hotspot instead.
- Keep software updated: Many wi fi attacks exploit vulnerabilities that patches have already fixed. Automatic updates ensure your devices maintain the latest protections against documented threats in the operating system.
- Use strong authentication: Implement strong, unique passwords for all online accounts with two-factor authentication enabled. Even if attackers steal sensitive information through a WiFi compromise, MFA provides a second line of defense.
- Clear browsing data: Clear browser history, cache, and cookies regularly when using public networks. Attackers can gain access to this information through network attacks, revealing your browsing patterns and potentially exposing stored credentials.
- Enable firewalls: Activate device firewalls to block incoming connection attempts. Software firewalls prevent attackers from directly accessing your device even when connected to the same network.
- Verify network legitimacy: Always check with the front desk or café staff to make sure the network name you see is the authorized one. This simple step helps avoid evil twin networks that mimic legitimate services.
How Can You Tell If You’re Connected to an Unsafe WiFi Network?

- Networks without password requirements represent immediate red flags. Any WiFi network offering public access without authentication lacks even basic security measures. While convenient, these open networks provide zero protection against monitoring.
- Suspicious network names that closely match legitimate networks may indicate an evil twin attack. Names like “Starbucks_Free_WiFi” versus “Starbucks Free WiFi” differ by a single character but may represent fake access points designed to steal sensitive information.
- Certificate warnings when browsing HTTPS sites indicate the possibility of a man-in-the-middle attack. If your browser displays SSL certificate errors on sites that normally work correctly, someone may be intercepting your internet traffic. Never ignore these warnings about public WiFi.
- Unusually slow connection speeds can signal compromised access points. Attackers running packet-sniffing software or routing traffic through their systems often cause noticeable performance degradation, as processing overhead slows data flow.
- Unexpected redirects to unfamiliar websites, especially pages that request login credentials, indicate a network compromise. Legitimate wi fi services use standardized captive portals, not suspicious-looking login pages hosted on random domains.
- Pop-up advertisements appearing on websites that normally don’t show ads suggest traffic injection. Attackers insert these ads into unencrypted traffic, both generating revenue and potentially delivering malware.
- Multiple networks with identical names in the same location indicate at least one fake access point. Attackers often clone legitimate network names, hoping users won’t notice multiple options.
- Your device showing two simultaneous connections suggests an evil twin attack. Most devices shouldn’t maintain multiple wi fi connections unless specifically configured for that purpose.
- Antivirus software or security software warnings about network threats require immediate attention. Modern security tools detect many WiFi-based attacks and alert users to potential compromises.
- Difficulty accessing secured websites while other sites work normally may indicate SSL stripping attacks. If HTTPS sites consistently fail to load while HTTP sites function properly, your connection is likely under active tampering.
How Can You Protect Your Data When Using Public WiFi?

- Layer your security measures rather than relying on single solutions. Combining VPN service use, HTTPS-only browsing, disabled file sharing, and restricted activities creates a defense-in-depth that withstands most attack types.
- Implement enterprise mobile device management for business phones and laptops. MDM solutions enforce security policies automatically, ensuring remote devices maintain proper configurations regardless of employee actions.
- Deploy always-on VPN configurations that prevent network access when VPN connections are inactive. This approach eliminates the risk of employees forgetting to activate VPN protection before accessing sensitive resources.
- Use cellular data for sensitive transactions whenever possible. Personal mobile hotspots provide secure connections without the risks of public WiFi. Many businesses now reimburse employees for mobile hotspot data usage as a security investment.
- Restrict public wi fi access based on risk assessment. Some organizations completely prohibit public network connections for devices accessing critical systems, accepting inconvenience as necessary for security.
- Monitor devices for compromise indicators after public wi fi exposure. IT security teams should regularly scan remote devices for malware, suspicious network configurations, and other indicators of successful attacks.
- Implement time-limited access controls for remote workers. Sessions that time out quickly limit the window attackers have to exploit stolen credentials or hijacked sessions.
- Require password changes immediately after a suspected public wi fi compromise. If employees believe their connection may have been compromised, immediate credential rotation prevents attackers from using captured passwords.
- Deploy endpoint detection and response software on all remote devices. EDR solutions identify and block attack behaviors in real-time, stopping many threats before they cause damage.
- Conduct regular security audits of remote work practices. Understanding how employees actually use public wi fi reveals gaps between policy and practice that require additional training or technical controls.
FAQs
Can public WiFi see what you are doing?
Yes, unencrypted public WiFi allows network operators and attackers to see your browsing activity, websites you visit, and data you transmit. Networks can log your device’s MAC address, connection times, bandwidth usage, and full browsing history for unencrypted sites. This monitoring occurs automatically through the network infrastructure, with no obvious signs to users.
However, using HTTPS for websites and virtual private network (VPN) encryption protects most of your activity. HTTPS encrypts the specific pages you visit and data you send, while VPNs encrypt everything, making your activity invisible to local network monitoring. Your ISP and VPN provider can still see which servers you connect to, but not the specific content you access.
Is connecting to hotel WiFi safe?
Hotel WiFi carries the same security risks as other public networks, despite appearing more trustworthy. Many hotels use outdated security protocols, infrequently changed shared passwords, and minimal network segmentation. Guests on the same network can monitor each other’s traffic using the attack methods described above.
Some hotels offer “premium” or “business” WiFi tiers with enhanced security, but these still operate as shared networks with numerous connected devices. Always use a VPN service when connecting to hotel WiFi, avoid sensitive transactions, and treat hotel networks as potentially compromised. Never conduct banking, access confidential work systems, or transmit private information without proper encryption.
Is it safe to check emails on public WiFi?
Checking email on public WiFi depends entirely on your email service’s security implementation and on whether you use additional protections. Modern email services like Gmail, Outlook, and Yahoo use HTTPS encryption for web access, protecting your login credentials and message contents from simple network monitoring. However, some older corporate email systems still use unencrypted connections.
The greater risk comes from credential theft, even when email access is encrypted. Attackers monitoring the network might capture passwords during initial login if HTTPS isn’t implemented correctly. We recommend using public wifi with a virtual private network before checking email on any public network, enabling two-factor authentication on your email account, and using dedicated email applications rather than web browsers when possible, as they often provide better security.
In Conclusion
Public WiFi networks pose significant security risks for businesses, but understanding these threats enables effective protection strategies. The combination of technical controls, such as virtual private network services and HTTPS, with strong security policies and employee training creates multiple layers of defense against most attacks.
Organizations cannot simply prohibit the use of public WiFi in our mobile-first business environment. Instead, accept that these security risks exist and implement comprehensive security measures that allow safe remote work. The costs of proper WiFi security pale in comparison to the average consequences of a breach, which average millions of dollars.
Employee education remains critical because human factors drive 68% of security incidents. Your team members must recognize rogue networks, understand attack indicators, and consistently follow security protocols. Technology alone cannot protect against threats that exploit vulnerabilities in human behavior.
We work with businesses nationwide to design secure network infrastructures that support remote work without compromising security. Our 19+ years of experience serving 20,000+ locations give us deep insight into protecting mobile workforces while maintaining operational efficiency. Contact us to discuss how proper network security planning, employee training, and technical controls can protect your business from public wi fi threats.
Citations:
[1] https://www.cloudwards.net/dangers-of-public-wifi/
[2] https://www.ibm.com/reports/data-breach
[3] https://www.pandasecurity.com/en/mediacenter/public-wifi-safety-survey/
[4] https://www.splunk.com/en_us/blog/learn/man-in-the-middle-attacks.html
[5] https://allaboutcookies.org/public-wifi-safety
[6] https://www.fortinet.com/resources/cyberglossary/man-in-the-middle-attack
[7] https://securelist.com/research-on-unsecured-wi-fi-networks-across-the-world/76733/
[8] https://www.techtarget.com/searchsecurity/definition/evil-twin
[9] https://en.wikipedia.org/wiki/Evil_twin_(wireless_networks)
[10] https://www.kaspersky.com/resource-center/definitions/what-is-session-hijacking


